Wed, Apr 1, 202615:44MCPSecurity
OWASP MCP Top 10 and the MCP Server Security Standard
John Van Lowe gives two lightning talks on MCP security: the OWASP Top 10 and the MSSS.
Takeaways
- The OWASP MCP Top 10 covers risks where MCP lets LLMs reach data sources and tools, often with no human in the loop: prompt injection, insufficient authentication, shadow MCP servers, context injection, secret exposure and tool poisoning.
- He walks a recent supply-chain compromise through those risks, from a package upgrade to command execution, exfiltration and token mismanagement.
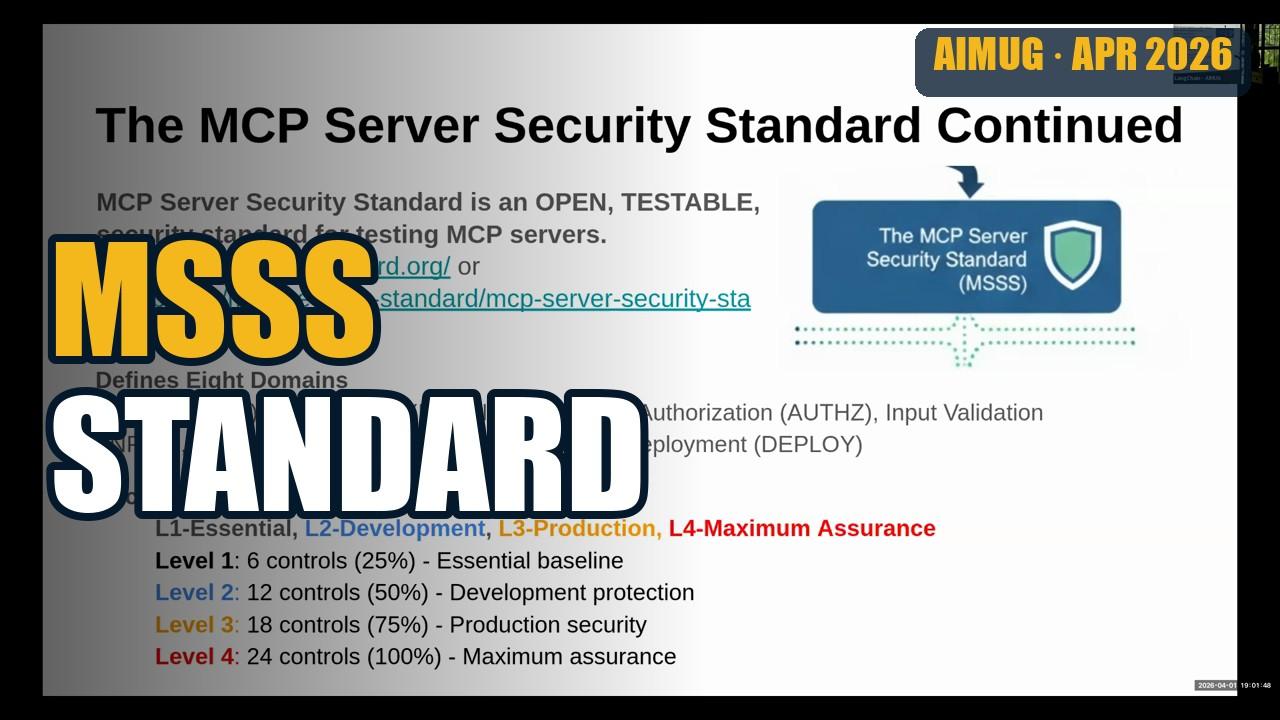
- The MCP Server Security Standard (MSSS) has eight domains and compliance levels from essential to maximum assurance, and he suggests developers meet at least the six essential controls.
- Controls map to threats: secret redaction, OAuth delegation, least privilege and RBAC, URL validation against server-side request forgery, container hardening, audit logging and file system sandboxing.
- He frames this against PCI DSS, SOC 2, ISO 27001 and FedRAMP, and points to VetSec, OWASP Austin and other groups for getting involved.
Transcript
Transcript coming.
Same night
 13:25BuildScript: A Website Built from a Google DocStefano Casafranca · Coding agents
 18:03GitKB: A Git-Like Knowledge Base for AI AgentsMatt Walters · Graphs
 15:15Safe Autonomous AI Systems: Lessons from Process ControlRiccardo Pirruccio · Agents
 15:12Spec-Driven Agent Coding: Specs as Source of Truth with forgectlJake Cukjati · Evals